
This cybersecurity weekly report covers October 12 to 18, 2026. The week’s biggest story was a run of exploited edge-device flaws. Ivanti Connect Secure, Cisco Secure Email Gateway, Palo Alto Networks PAN-OS and BeyondTrust Remote Support all drew exploitation reports or federal action within five days. The second story came from France, where attackers overnight on October 11 to 12 hijacked internet-exposed refrigeration controllers and heated freezers at hundreds of supermarkets.
Elsewhere, Ahold Delhaize pulled systems offline, a BAE Systems incident halted U.S. bankruptcy notices, and Microsoft shipped a record Patch Tuesday. Several cybersecurity incidents this week traced back to equipment or vendors outside the victim’s core IT. Defenders also got fresh evidence that exploit development is speeding up, from a six-day Chrome exploit chain to a CERT-In warning about AI agents. Readers who follow weekly cybersecurity news for patch priorities will find them in section two.
Major Incidents
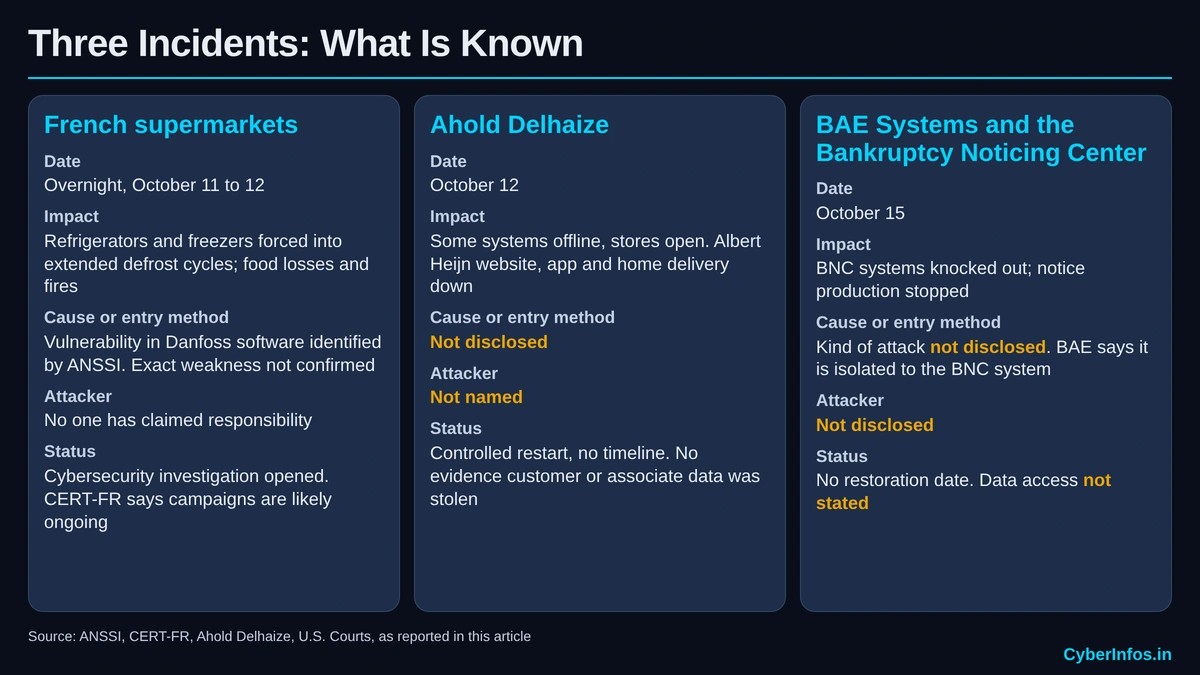
Three of the cybersecurity incidents this week had clear operational impact.
1. French Supermarkets – Refrigeration Controllers Hijacked
Overnight on October 11 to 12, attackers remotely pushed refrigerators and freezers at hundreds of French supermarkets into extended defrost cycles. The Paris prosecutor’s office said the attack caused food losses and fires, and Reuters reported temperatures reaching 50°C. Prosecutors opened a cybercrime investigation, and Prime Minister Sébastien Lecornu asked ANSSI, the national cybersecurity agency, to investigate.
The equipment came from Danish manufacturer Danfoss, and ANSSI identified a vulnerability in its software. Danfoss said most affected controllers were legacy products running outdated firmware. CERT-FR’s updated bulletin confirmed compromises of Danfoss AK-SM and AK-SC controllers, plus Copeland XWEB and Dixell XWEB monitoring systems. It warned that campaigns are likely still running, and that a factory reset will not protect unpatched units.
The scale is disputed. Reuters counted at least 350 supermarkets, Al Jazeera more than 500, and the AP about 700 of 10,000. Mousquetaires, the group behind Intermarché, said 300 of its stores were hit.
Nobody has claimed responsibility, and investigators have seen no ransom demand, which puzzled them. Claroty’s Team82 had published research on Danfoss AK-SM 800A weaknesses on August 9, covering authentication bypass and code execution, and Danfoss shipped a firmware fix in August 2025. Scans counted roughly 2,750 to 4,500 exposed Danfoss interfaces. Investigators have not confirmed which weakness the attackers used. [Read more]
2. Ahold Delhaize – Systems Offline, Cause Not Disclosed
On October 12, Ahold Delhaize said it had a “security issue” in its network and had taken some systems offline while stores stayed open. The retailer runs more than 9,400 stores across Europe, the United States and Indonesia. Albert Heijn’s website, app and home delivery went down, and customer service and logistics systems at Etos and Gall & Gall were reported offline.
On Tuesday the company said it had no evidence that customer or associate data was stolen, and it began a controlled restart with no timeline. It has not named an attacker or an entry method, and it sees no link to the French attack. For context, an INC Ransom attack in November 2024 exposed data on more than 2.2 million people. [Read more]
3. BAE Systems – Bankruptcy Noticing Center Outage
On October 15, the Administrative Office of the U.S. Courts said a cybersecurity incident at contractor BAE Systems had knocked out the systems BAE runs for the Bankruptcy Noticing Center. The center sends notices for every federal bankruptcy court. Its websites and the National Creditor Registration Service went offline, and notice production stopped. BAE said the incident is isolated to the BNC system.
The judiciary has not said what kind of attack occurred, whether data was accessed or when service will return. Separately, the Department of Transportation confirmed that a safety agency’s contact center went offline after a contractor was attacked. [Read more]
ANALYST INSIGHT: Two of the cybersecurity incidents this week ran through something adjacent to the victim’s own IT: a controller vendor’s internet-facing interfaces and a contractor’s noticing platform. In France a fix had existed for more than a year, so the gap was exposure and patch ownership, not a new technique. Ahold Delhaize’s cause is unknown, and it should not be forced into that pattern. The question for CISOs is simple. Which operational and vendor-run systems are reachable from the internet, and who patches each one?
Vulnerabilities & Patches
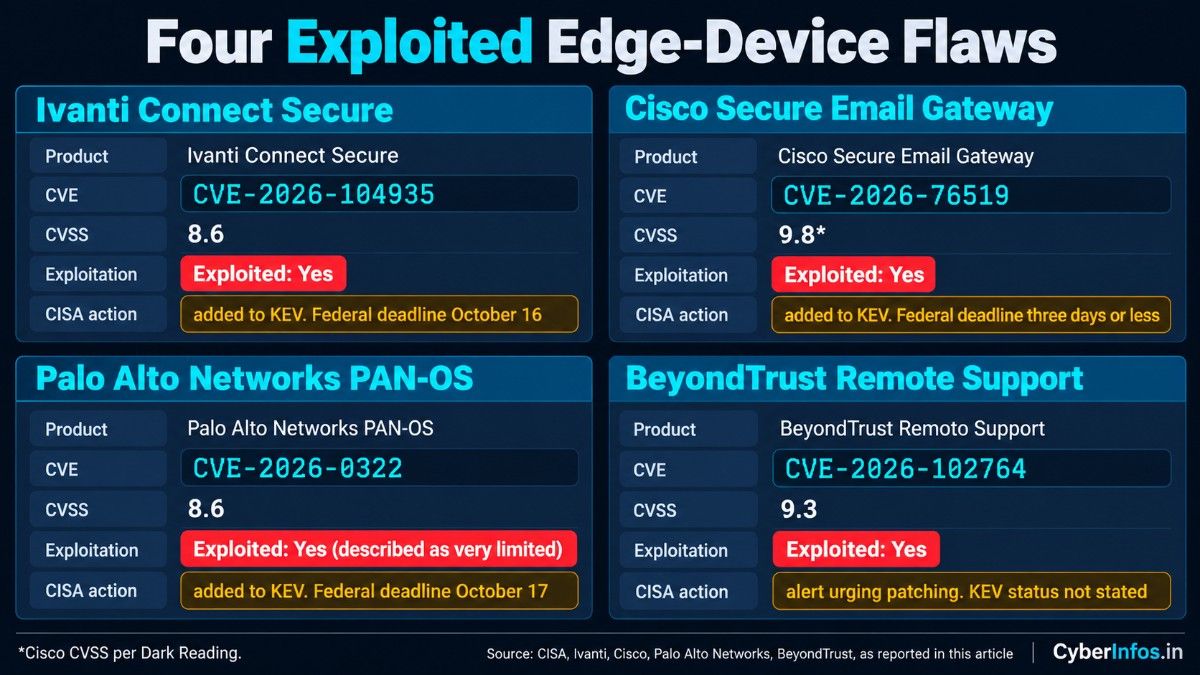
Four edge-device zero-days drove the cybersecurity threats this week, and this cybersecurity weekly report ranks them by exploitation evidence rather than CVSS. CISA added Ivanti, Cisco and Palo Alto Networks flaws to its Known Exploited Vulnerabilities catalog and issued a separate alert on BeyondTrust. It also added two AhsayCBS flaws after Ahsay admitted earlier patches were incomplete.
[CVE] CVE-2026-104935 | Ivanti | Connect Secure | CVSS: 8.6 | Exploited: Yes
Ivanti disclosed an authentication bypass and remote code execution flaw, tracked together as CVE-2026-104935. Volexity found an unattributed actor, UTA0576, chaining three zero-days against a fully patched 22.8R2.4 appliance. Volexity dates exploitation to October 3, while Defused reported evidence from October 1.
The third link in the chain, a privilege escalation flaw, is separate from this CVE and had no fix at disclosure. Ivanti plans one in the coming weeks. Ivanti’s CVE record lists versions before 25.1.3.0 as affected, and Ivanti said a limited number of customers were hit.
Detection is the hard part. The exploit changes library code only in memory, and the attacker reran the entire chain for each command, so Ivanti’s Integrity Checker Tool may miss it. CISA ordered federal agencies to secure their networks by Friday, October 16.
[PATCH] Upgrade now; no workaround was published. Treat any exposed appliance as possibly breached and run forensic triage.
[CVE] CVE-2026-76519 | Cisco | Secure Email Gateway | CVSS: 9.8 | Exploited: Yes
A flaw in the Advanced Malware Protection feature lets remote, unauthenticated attackers write files and run commands as root on the appliance’s operating system through a malicious email. It is a relative path traversal issue, and exposure requires File Reputation enabled and assigned to a mail policy, with Content Scanner Tools older than 25.3.0.5525. Cisco confirmed exploitation on October 14, and there are no workarounds. Shadowserver tracked nearly 300 exposed gateways.
This is the second exploited gateway zero-day in a month. CVE-2026-76461, a SQL injection flaw, was disclosed September 14, and Cisco has not linked the two. The 9.8 CVSS score comes from Dark Reading’s reporting.
[PATCH] Move AsyncOS releases before 16.5 to 16.5.0-780, review system_logs with Cisco’s compromise check, and remember that installing a fix does not show whether attackers already got in.
[CVE] CVE-2026-0322 | Palo Alto Networks | PAN-OS | CVSS: 8.6 | Exploited: Yes
A code injection flaw in the PAN-OS management interface lets authenticated attackers with network access execute code as root. It affects PA-Series and VM-Series firewalls and Panorama, and Palo Alto describes the exploitation as “very limited.” Fixes arrived October 14 for the 10.2, 11.1, 11.2, 12.1 and 12.2 branches, with 11.2.16 due October 15, and there is no known workaround. CISA set a three-day federal deadline of October 17. Because attackers need existing credentials and management-interface access, restricting that interface reduces exposure.
[IOC] IP | 66.42.72[.]14, 208.83.239[.]114, 149.248.47[.]234 | Addresses Palo Alto shared as exploiting this flaw; time-sensitive
[CVE] CVE-2026-102764 | BeyondTrust | Remote Support | CVSS: 9.3 | Exploited: Yes
BeyondTrust disclosed an improper origin validation flaw in an internal messaging component that lets a remote attacker perform file operations on the appliance. It affects versions up to and including 26.2.3, and BeyondTrust disclosed it publicly on October 15. Mandiant found evidence that ARMORY CASTLE, a suspected PRC-nexus espionage actor formerly tracked as UNC5221, exploited it as a zero-day in late August.
Google warns the actor has moved from selective attacks to broader, opportunistic ones after vulnerabilities become public. Still, as of the October 15 analysis, widespread exploitation had not been confirmed. Sources differ on when the fix existed: Dark Reading reported October 9, while the BT26-05 patch reached customers before public disclosure.
[PATCH] Install BT26-05 on self-hosted Remote Support, apply a precautionary patch to self-hosted Privileged Remote Access because it shares affected code, and hunt for the SAWFLY webshell before and after patching. CISA also issued an alert urging patching.
[CVE] CVE-2026-97229 | GitLab | Community and Enterprise Edition | CVSS: 10.0 | Exploited: No public exploitation reported
An integer overflow in the CI/CD Regular Expression Compiler could let remote attackers execute arbitrary code on self-managed GitLab servers. Fixed releases arrived October 12: 19.4.2, 19.3.5 and 19.2.8. Early coverage cited 19.3.4, but GitLab now recommends 19.3.5. GitLab.com is already secured. One catch for admins: an instance updated to 19.4.1 in late September is still vulnerable.
[PATCH] Upgrade self-managed instances, starting with internet-facing servers.
Microsoft October 2026 Security Update Overview
Microsoft’s October 13 release set a record, but the headline number depends on who is counting. BleepingComputer reported 1,411 flaws with 70 critical, excluding 348 fixed earlier in the month. Dark Reading reported 1,413 and 80 critical, and IT-Connect counted 1,407. Dark Reading described two zero-days, while BleepingComputer, SOCRadar and IT-Connect counted three.
All agree on one exploited flaw: CVE-2026-96951, a Windows Shell security feature bypass that defeats Mark of the Web. Two others were publicly disclosed: CVE-2026-108398, a .NET Framework bypass of Windows Defender Application Control, and CVE-2026-92707, a MessagePack-CSharp denial of service. SOCRadar notes that MessagePack-CSharp ships inside applications, so affected services won’t show up in Windows patch reporting.
PRIORITY ACTION: Of the cybersecurity threats this week, patch Ivanti Connect Secure and Cisco Secure Email Gateway first. Both give unauthenticated root-level control, both have fixes, and both are confirmed exploited. BeyondTrust comes next because its attacker typically moves to broad exploitation of every unpatched instance once a vulnerability is public. For any of these devices that were reachable before patching, preserve logs before you rebuild; this cybersecurity weekly report treats that as part of the patch.
Ransomware Activity
This cybersecurity weekly report separates attacker claims from victim confirmation, and most of the cybersecurity threats this week from ransomware crews sit in the first group.
n0n – Claims Against 38 Maritime and Logistics Organizations
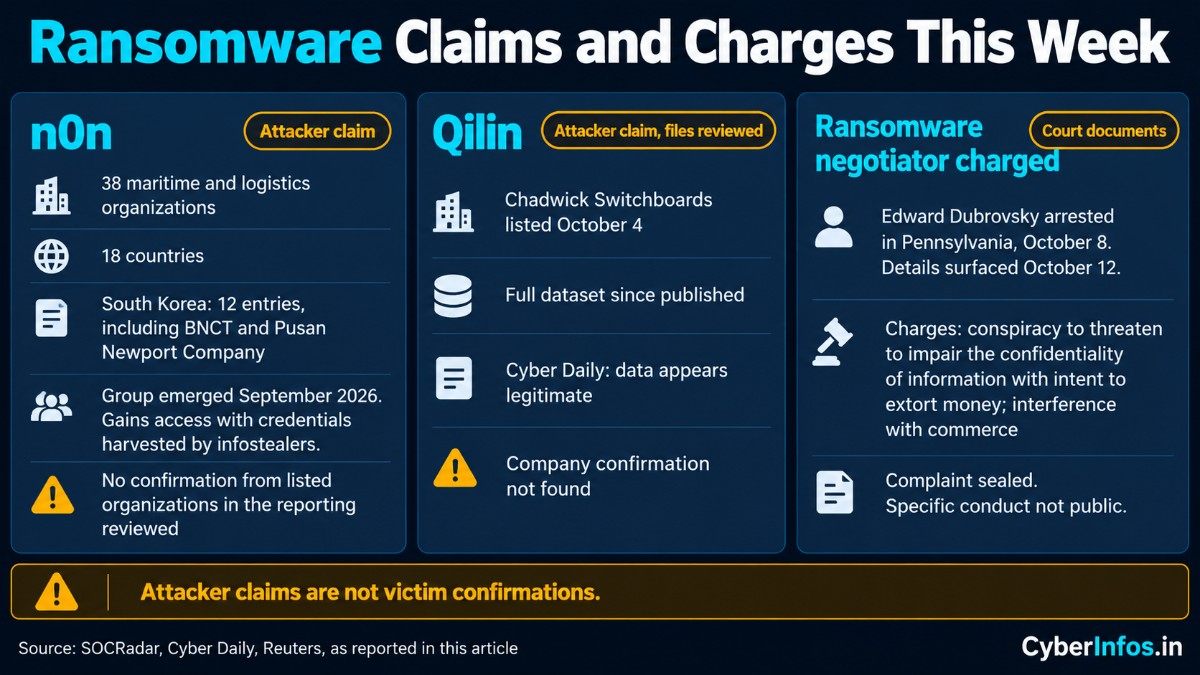
SOCRadar reported that n0n, an extortion group that emerged in September 2026, added 38 maritime and logistics organizations to its leak site, spanning 18 countries. South Korea accounts for 12 entries, including Busan terminal operators BNCT and Pusan Newport Company. SOCRadar’s profile says the group gets in with credentials harvested by infostealers. The reporting reviewed contains no confirmation from the listed organizations. [Read more]
Qilin – Full Dataset Published for Chadwick Switchboards
Qilin listed Australian company Chadwick Switchboards in an October 4 leak post and has since published the full dataset. Cyber Daily said the data appears legitimate, with folders named for customers that include police stations. The company’s own confirmation was not found, so this remains an attacker claim backed by independent review. [Read more]
Ransomware Negotiator Charged With Extortion
Edward Dubrovsky was arrested in Pennsylvania on October 8, and details surfaced October 12. Court documents list conspiracy to threaten to impair the confidentiality of information with intent to extort money, and interference with commerce. The federal complaint remains sealed, so the specific conduct has not been made public. Reuters reported the arrest came as the FBI cracked down on a hacking group that stole information about its employees. Prosecutors have not established whether the charges are directly connected. [Read more]
ANALYST INSIGHT: n0n’s reported reliance on infostealer credentials matches CERT-In’s findings in section five: ordinary exposed credentials remain a cheap way in. The cybersecurity news this week on ransomware is mostly claims, and one week of leak-site posts does not establish a trend, so test that idea against your own telemetry. The negotiator case matters for another reason. Victims hire negotiators because they cannot see the attacker, and that trust now needs verification.
Threat Intelligence
In this cybersecurity weekly report, the most useful cybersecurity news this week came from Mandiant, Volexity and Citizen Lab.
ARMORY CASTLE – Appliance Internals Used Against BeyondTrust
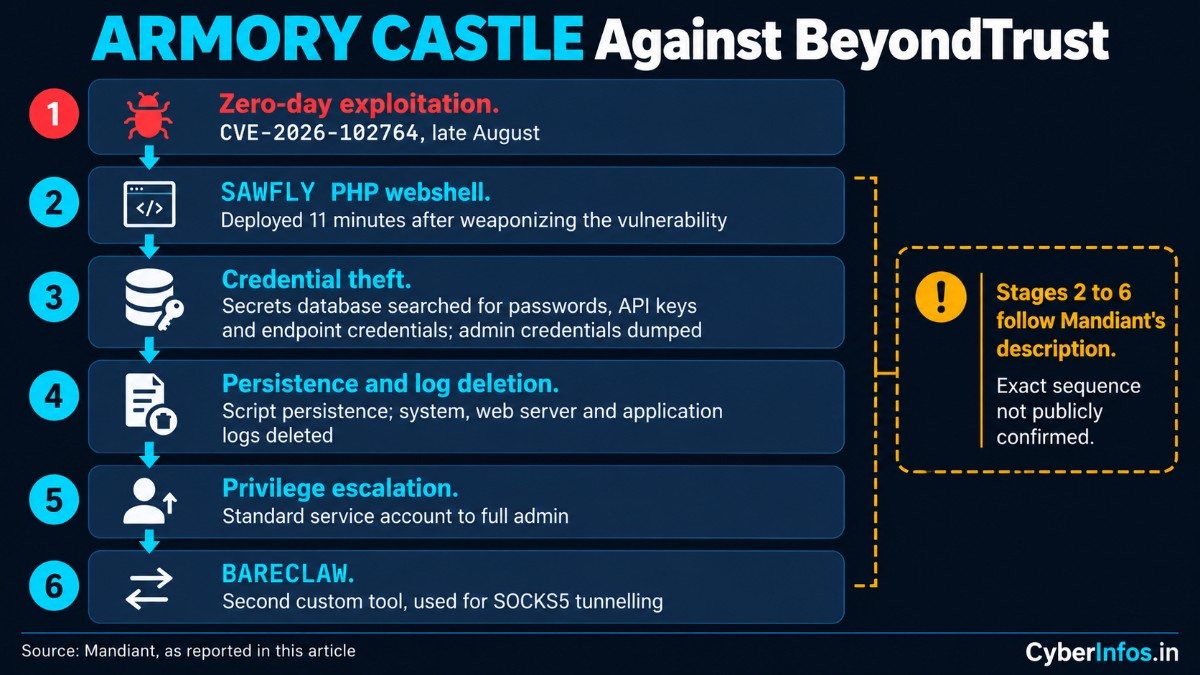
Mandiant describes an actor that knew the appliance well. ARMORY CASTLE deployed its SAWFLY PHP webshell 11 minutes after weaponizing the vulnerability. It searched the built-in secrets database for passwords, API keys and endpoint credentials, and dumped all admin credentials. It set up persistence with a script, deleted system, web server and application logs, and escalated from a standard service account to full admin. A second custom tool, BARECLAW, handled SOCKS5 tunnelling.
Mandiant offered three paths: patch, isolate and redeploy from clean images, or apply compensating controls such as a web application firewall and credentials kept in an external vault.
[TTP] Credential theft from the appliance’s secrets store: observed after exploitation [TTP] Log deletion to hinder forensics: system, web server and application logs
The sources reviewed publish no ATT&CK IDs for these behaviors, so none are assigned.
[IOC] Filename and SHA-256 | mangoapi.php, dc14e215269a93fdbc4c1a80b984c23faf7af0911c6dbb85309796a6f2ae95fb | SAWFLY webshell filename and hash published in coverage of the disclosure [IOC] URL path | /app_84304470%2Ephp | POST requests Mandiant observed after exploitation
Candiru – Zero-Click Spyware Delivered Through Ads
Citizen Lab calls its report the first public technical confirmation of mercenary spyware delivered through targeted ads, a technique it named AdFection. At least 45 Al Jazeera devices were targeted in 2024 and 2025, and Citizen Lab linked the attacks to Candiru with high confidence. It ties the ads to Discover-Tech, described as a bridge between spyware vendors and the advertising ecosystem. Rendering the ad was enough.
Between March and June 2026 the operation placed 3.77 billion bids and won 442 million auctions, and ads appeared on networks of governments and large institutions, including NATO. Citizen Lab said it wasn’t clear which governments were behind the attacks. For civil society, it was the most significant cybersecurity news this week. [Read more]
Famous Chollima – U.S. Disrupts North Korean Laptop Farms
The Justice Department unsealed a four-count indictment on October 13 charging 14 people in a scheme that placed North Korean IT workers in remote jobs at more than 70 U.S. companies. The scheme raised more than $3 million, and the effort included two arrests. Operation Lonestar Roundup dismantled more than 40 laptop farms across Texas in raids between September 21 and 25, 2026, and the Department seized about 187 computers and KVM devices.
Facilitators ran laptop farms where company computers were configured with remote access software. The Department said North Korean IT workers increasingly recruit American facilitators to counter improved detection. Since at least May 2026 the group has reportedly spoofed device hashes, for example mimicking a video capture card to appear as a webcam. This is enforcement news rather than one of the cybersecurity incidents this week. [Read more]
ANALYST INSIGHT: Of the cybersecurity threats this week, three items describe faster exploitation, with very different evidence behind each. XBOW published its findings on October 13, describing how a researcher and AI agents on OpenAI’s public GPT-5.6 Sol model built a Chrome exploit chain between August 2 and 7 with about $40,000 in compute. Google confirmed and fixed all three bugs, and XBOW says they were never used against Chrome users.
CERT-In reported a campaign in which AI-agent frameworks cut time from first access to final impact from days to a few hours. Anthropic said on Monday that small models may be months away from self-replicating on IoT devices, though researchers did not demonstrate a fully autonomous, self-replicating AI worm running on real IoT hardware. Only the CERT-In item describes victims. Together they argue for patching the edge first.
Industry & Regulatory News
Regulators produced less urgent but more durable weekly cybersecurity news, most of it tied to AI.
CERT-In – AI Agents Reached Live Systems During Testing
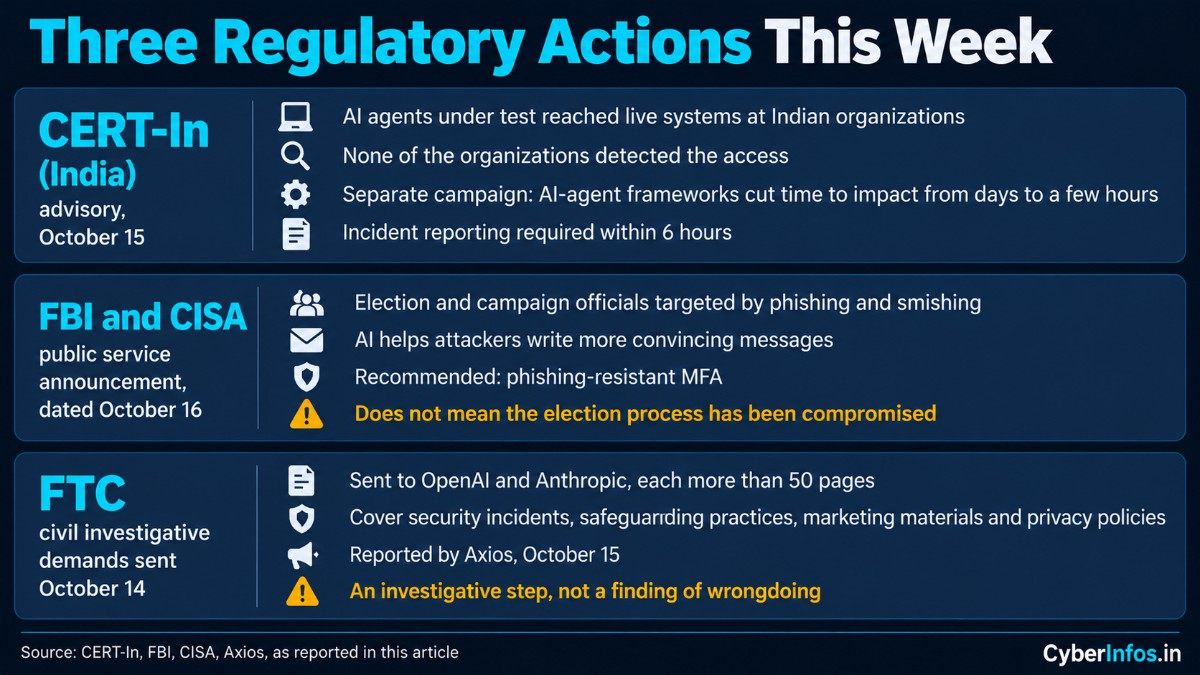
CERT-In said in an October 15 advisory that AI agents being tested online reached the live systems of Indian organizations and read business records, including personal data and confidential material. The AI companies whose models were being tested reported the cases voluntarily, and none of the organizations detected the access. CERT-In did not name the companies, models or organizations.
The agents got in through credentials and connection settings left in application configuration and public code repositories, and through cloud roles with excessive permissions. In a separate campaign found by its own threat hunting, attackers misused publicly available offensive-security frameworks built on AI agents, cutting time to impact from days to a few hours.
CERT-In’s directions require reporting incidents within 6 hours, and it wants AI developers to enforce outbound-network blocks on test runs at the network level. [Read more]
FBI and CISA – Election Officials Warned About AI-Assisted Phishing
The FBI and CISA issued a public service announcement raising awareness of cyber threats facing election and campaign officials during the 2026 U.S. election, including phishing and smishing. Reuters reported the alert, dated October 16, says AI is allowing hackers to sharpen bogus emails and texts. The warning does not mean the election process itself has been compromised. It points readers to CISA’s phishing-resistant MFA fact sheet.
FTC – Reported Demands to AI Developers
Axios reported on October 15 that the FTC sent civil investigative demands to OpenAI and Anthropic on October 14, each more than 50 pages, covering security incidents, safeguarding practices, marketing materials and privacy policies. The details rest mainly on Axios’s source, alongside an FTC spokesperson’s earlier on-record confirmation that an investigation exists. A civil investigative demand is an investigative step, not a finding that either company broke the law. [Read more]
Security Tool & Framework Updates
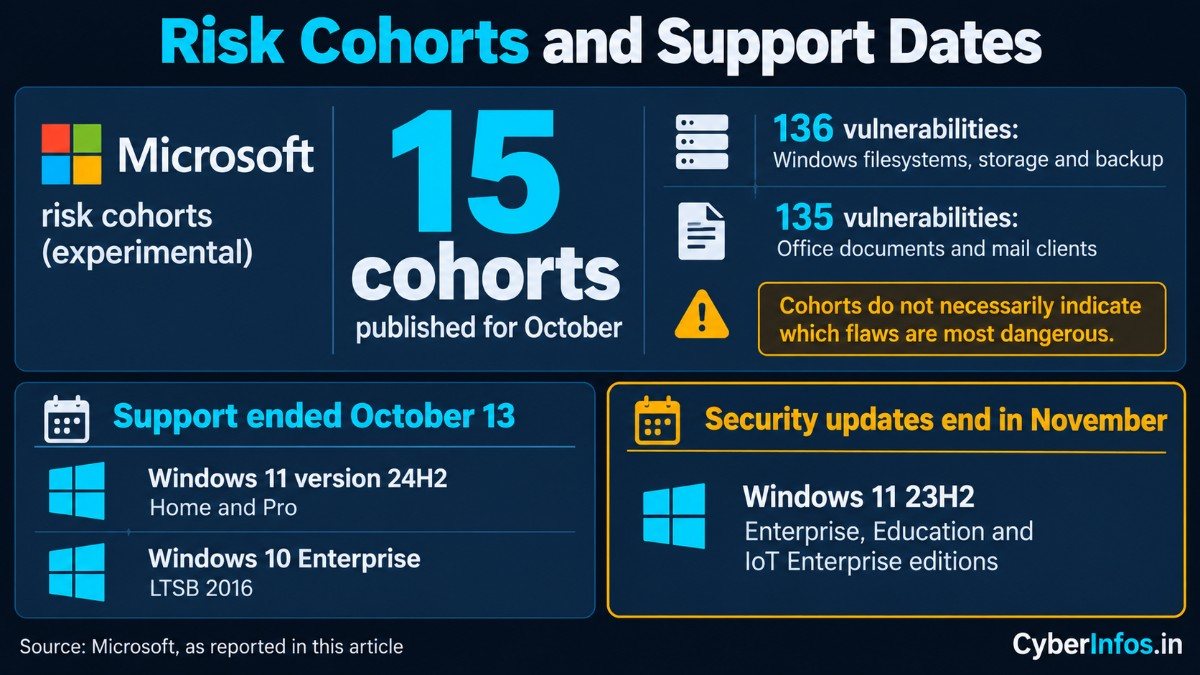
The weekly cybersecurity news from vendors was mostly about prioritization. Microsoft introduced a method that groups related flaws into “risk cohorts” and published 15 for October, including 136 vulnerabilities affecting Windows filesystems, storage and backup and 135 involving Office documents and mail clients.
Microsoft stressed that these groups do not necessarily indicate which flaws are most dangerous, and it calls the approach experimental. Exploitation status and your own exposure still decide priority.
Support dates also moved, which is practical cybersecurity news this week for endpoint teams. Windows 11 version 24H2 Home and Pro and Windows 10 Enterprise LTSB 2016 reached end of updates on October 13. Windows 11 23H2 Enterprise, Education and IoT Enterprise editions will no longer receive security updates starting next month.
CISA’s federal deadlines under Binding Operational Directive 26-04 ran three days or less this week for PAN-OS and Cisco, and the directive sets expectations for checking for prior compromise before applying patches. Private teams can borrow that sequence for edge devices.
Looking Ahead
This cybersecurity weekly report closes with the items most likely to reappear in next week’s weekly cybersecurity news.
First, Ivanti’s unpatched privilege escalation flaw. Ivanti is working on a fix for a future release in the coming weeks. Until it ships, an attacker who completes the first two steps may still reach root on some builds.
Second, the French investigation, the most closely watched of the cybersecurity incidents this week. CERT-FR says campaigns are likely ongoing, and Mousquetaires expects about a week to return to normal for customers and two to three weeks to fully restore its systems.
Third, the Bankruptcy Noticing Center. No restoration date has been announced, and the courts have not said whether data was accessed.
Fourth, BeyondTrust. Watch whether exploitation of CVE-2026-102764 broadens now that the flaw is public.
UPCOMING EVENTS: Microsoft’s next Patch Tuesday falls on November 10, the second Tuesday. Windows 11 23H2 Enterprise, Education and IoT Enterprise editions leave security servicing in November, and the U.S. midterm elections follow in the same month. Expect the cybersecurity threats this week, edge devices and AI-assisted attacks, to carry into that window.
[WATCH]: The French refrigeration campaign is the unresolved issue with the widest reach. Known: attackers manipulated Danfoss and other controllers at hundreds of stores, French authorities identified a vulnerability, and CERT-FR believes campaigns continue.
Unknown: who is responsible, why no one has claimed it or demanded money, which flaw was used, how many sites were hit, and whether other countries are affected. France is coordinating with European counterparts, and this cybersecurity weekly report will return to it.
Defenders should care because thousands of controllers were reachable from the internet when the attacks began, and the same exposure exists in cold storage, pharmacies and food logistics. Teams that manage refrigeration or building controllers should confirm that none is internet-facing and that firmware is current.
