
Software engineering teams, cloud infrastructure groups, and security operations centers (SOCs) are dealing with one of the largest automated CI/CD supply-chain and cloud-identity compromises recorded in 2026. Between November 10 and 13, 2026, an attacker weaponized stolen credentials for 4,837 hijacked developer accounts on GitHub to probe more than 61,764 repositories.
The same operator then ran the wfx GitHub Actions secret stealer in at least 1,806 to 1,835 of them, according to research from Aikido Security and SafeDep reported by The Hacker News, BleepingComputer, and SecurityWeek.
The danger goes well beyond stolen repository variables. Unlike conventional CI/CD credential harvesters, this payload exchanges OpenID Connect (OIDC, an identity protocol that lets GitHub Actions workflows log into cloud providers without static passwords) tokens to reach Amazon Web Services (AWS), Microsoft Azure, and Google Cloud Platform (GCP).
It then plants cloud identity backdoors built to survive credential rotation, as detailed by Chainguard and Phoenix Security.
Defenders should audit GitHub audit logs, Entra ID federated credentials, and AWS IAM role trust policies right away.
Quick Answer
The wfx GitHub Actions secret stealer (wfx-loot) is an active supply-chain campaign. Starting November 10, 2026, it used 4,837 compromised GitHub accounts to open wfx-docs test pull requests across 61,764+ repositories, inject malicious CI workflows into 8,093 repositories, and steal secrets from 1,806+ repositories. Along the way, it backdoored AWS IAM roles and Azure Entra ID apps (wfx-ci-*) through OIDC tokens.
What Happened and Incident Timeline
The campaign began around 12:45 UTC on Tuesday, November 10, 2026, and kept running through November 12 and 13. Per Chainguard and Barrier Networks, an automated pipeline fed stolen GitHub tokens and bot credentials into an engine built to probe repositories and harvest secrets.
Confirmed Facts
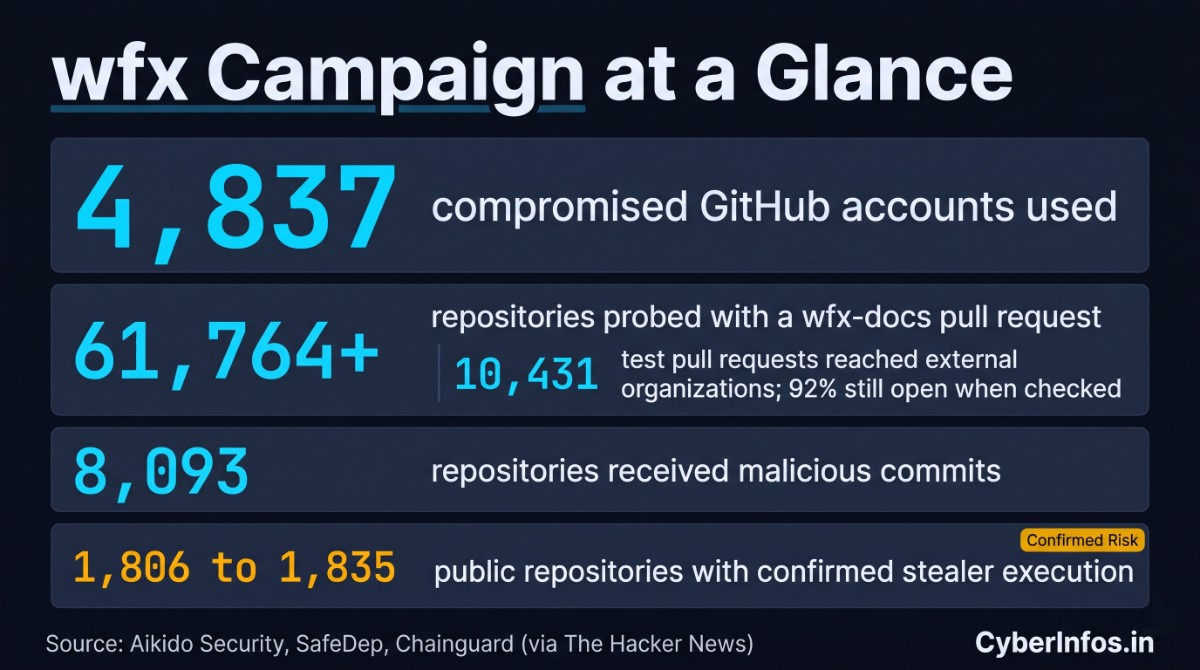
- Probing 61,764+ Repositories via wfx-docs Branches: Aikido Security and SafeDep, as reported in The Hacker News and Chainguard, found that the attacker used 4,837 compromised GitHub accounts to open a wfx-docs pull request probe across 61,764 repositories. The pull request was titled docs: dependency audit notes and came from a branch named wfx-docs. Barrier Networks puts the total at 63,000+ pull requests. Notably, 10,431 of the test pull requests landed in external organizations through collaborator or org access, and 92% were still open when checked.
- Malicious Commits in 8,093 Repos and Execution in 1,806+ Repos: SafeDep counted 8,093 public repositories that received malicious commits between 12:46 UTC on November 10 and 04:36 UTC on November 12. Aikido confirmed stealer execution in 1,806 to 1,835 public repositories, per Phoenix Security.
- 1,000x Overlap With October’s GhostAction Victims: Accounts hit in October’s GhostAction wave were roughly 1,000 times more likely to be reused in November. In 100+ repositories, the wfx payload was appended onto October’s GhostAction workflow files, per The Hacker News.
- Downstream Bot and Package Impact (wdio-bot and neuronai-studio): The stealer touched 28 WebdriverIO repositories through the hijacked bot wdio-bot, although no WebdriverIO release was affected. It also reached Packagist package digitalelvis/neuronai-studio version 3.14 through automated publishing, per Chainguard. At least 50 compromised accounts maintain packages on npm, PyPI, Go, Packagist, and crates.io.
Reported or Unconfirmed Claims
- Attribution Gap: Aikido told The Hacker News that it does not attribute wfx to the GhostAction actor, because the tools and infrastructure differ and stolen credentials are often resold.
- Private Repository Count: Researchers scanned only public repositories, although wfx includes settings for private repositories.
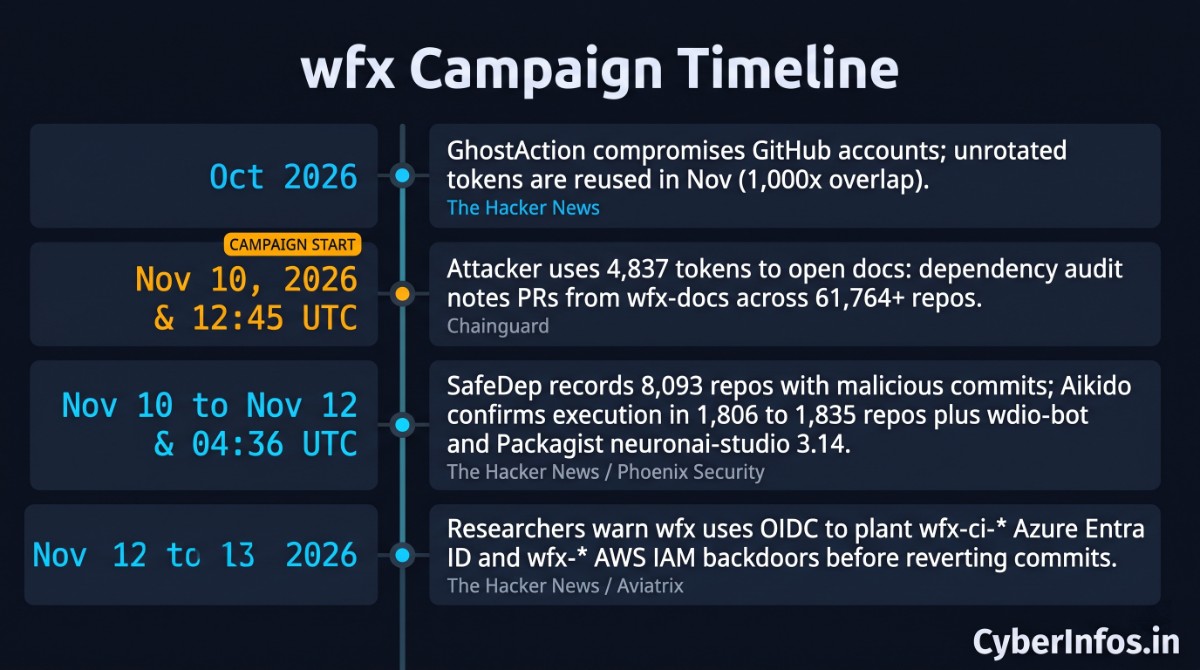
The table below outlines the confirmed chronological sequence of the wfx campaign.
| Date / UTC Time | Milestone / Event | Source |
|---|---|---|
| Oct 2026 | GhostAction compromises GitHub accounts; unrotated tokens are reused in Nov (1,000x overlap). | The Hacker News |
| Nov 10, 2026 (12:45 UTC) | Attacker uses 4,837 tokens to open docs: dependency audit notes PRs from wfx-docs across 61,764+ repos. | Chainguard |
| Nov 10 to Nov 12 (04:36 UTC) | SafeDep records 8,093 repos with malicious commits; Aikido confirms execution in 1,806 to 1,835 repos plus wdio-bot and Packagist neuronai-studio 3.14. | Phoenix Security |
| Nov 12 to 13, 2026 | Researchers warn wfx uses OIDC to plant wfx-ci-* Azure Entra ID and wfx-* AWS IAM backdoors before reverting commits. |
Aviatrix |
Facts at a Glance
The table below summarizes the verified technical attributes of the wfx (wfx-loot) campaign.
| Field | Verified Information |
|---|---|
| Campaign Name | wfx / wfx-loot GitHub Actions CI Secret Stealer and Cloud OIDC Backdoor Campaign (No CVE ID) |
| Targeted Platforms | GitHub Actions Runners, AWS IAM, Microsoft Entra ID, GCP, HashiCorp Vault, and registries (Packagist, npm, PyPI, Go, crates.io) |
| Confirmed Scale | 4,837 hijacked accounts; 61,764 to 63,000+ repos probed (10,431 via collaborator access); 8,093 repos committed; 1,806 to 1,835+ executed |
| Attack Type | CI/CD Workflow Injection, Runner Memory/Metadata Scraping, Cloud OIDC Trust Persistence |
| Campaign Status | Active in the Wild (started Nov 10, 2026 at 12:45 UTC; ongoing Nov 12 to 13) |
| CISA KEV Status | N/A (Supply-chain credential campaign rather than a single CVE) |
| Attribution | Unattributed; reuses October GhostAction victim credentials (1,000x overlap) |
| Remediation | Revoke GitHub tokens, rotate secrets, and remove wfx-ci-* Entra ID and wfx-* AWS IAM trust backdoors |
Affected and Fixed Versions
The table below maps affected repositories and packages verified by Chainguard and The Hacker News.
| Component / Package | Affected Scope | Safe State | Required Mitigation |
|---|---|---|---|
| GitHub Repositories | 61,764+ probed (wfx-docs); 8,093 committed; 1,806+ executed | Commits removed and OIDC trust audited | Audit Git reflogs, revoke tokens/SSH keys, and rotate secrets |
| Packagist digitalelvis/neuronai-studio | Version 3.14 per Chainguard |
Prior clean builds | Block 3.14 and rotate keys on hosts that installed it |
| WebdriverIO (wdio-bot) | 28 WebdriverIO repos touched | No package releases affected per The Hacker News | Rotate wdio-bot credentials and audit commits |
Technical Attack Chain
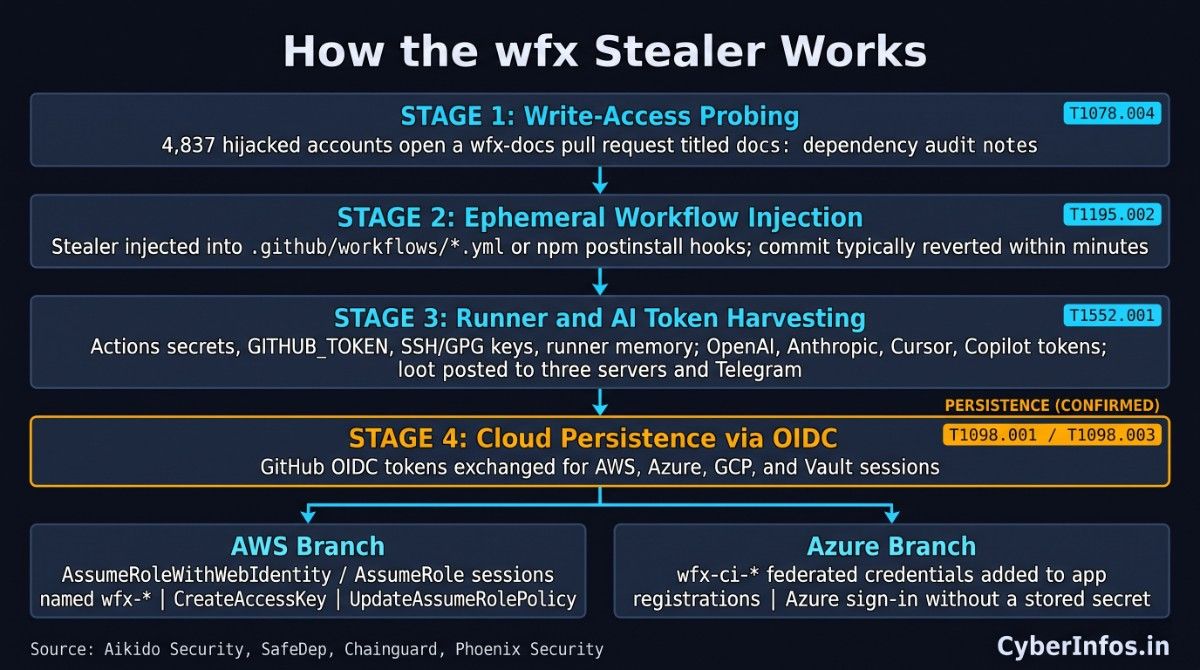
1. How the CI Secret Stealer Probes, Harvests, and Backdoors Cloud Accounts
Per Aikido Security, SafeDep, Chainguard, and Phoenix Security, the wfx GitHub Actions secret stealer operates in four stages:
- Write-Access Probing (MITRE ATT&CK T1078.004, Cloud Accounts): Using credentials from 4,837 hijacked developer accounts, automation opens a wfx-docs pull request probe (docs: dependency audit notes from wfx-docs) across every repository those accounts can reach. That includes 10,431 cross-organization pull requests.
- Ephemeral Workflow Injection (T1195.002, Compromise Software Supply Chain): Where a repository is writable, the pipeline injects the stealer into
.github/workflows/*.ymlor npm postinstall hooks. It typically reverts the commit within minutes of execution, so the branch looks clean. - Runner & AI Token Harvesting (T1552.001): Inside the runner, wfx scrapes Actions secrets, GITHUB_TOKEN, SSH/GPG keys, runner memory, and self-hosted metadata, Docker, and systemd state. It also grabs OpenAI, Anthropic, Cursor, and Copilot tokens, then posts the loot to three servers and Telegram.
- Cloud Persistence via OIDC (T1098.001 / T1098.003): The payload exchanges GitHub OIDC tokens for live AWS, Azure, GCP, and Vault sessions.
- AWS IAM Persistence: The payload establishes AWS AssumeRole trust policy persistence through AssumeRoleWithWebIdentity / AssumeRole sessions named
wfx-*. It then calls CreateAccessKey for IAM users and UpdateAssumeRolePolicy to open the role’s trust policy to any AWS account. - Azure Entra ID Persistence: It plants a wfx-ci federated identity backdoor by adding
wfx-ci-*federated credentials to Azure AD app registrations, which lets workflows sign into Azure without a stored secret.
- AWS IAM Persistence: The payload establishes AWS AssumeRole trust policy persistence through AssumeRoleWithWebIdentity / AssumeRole sessions named
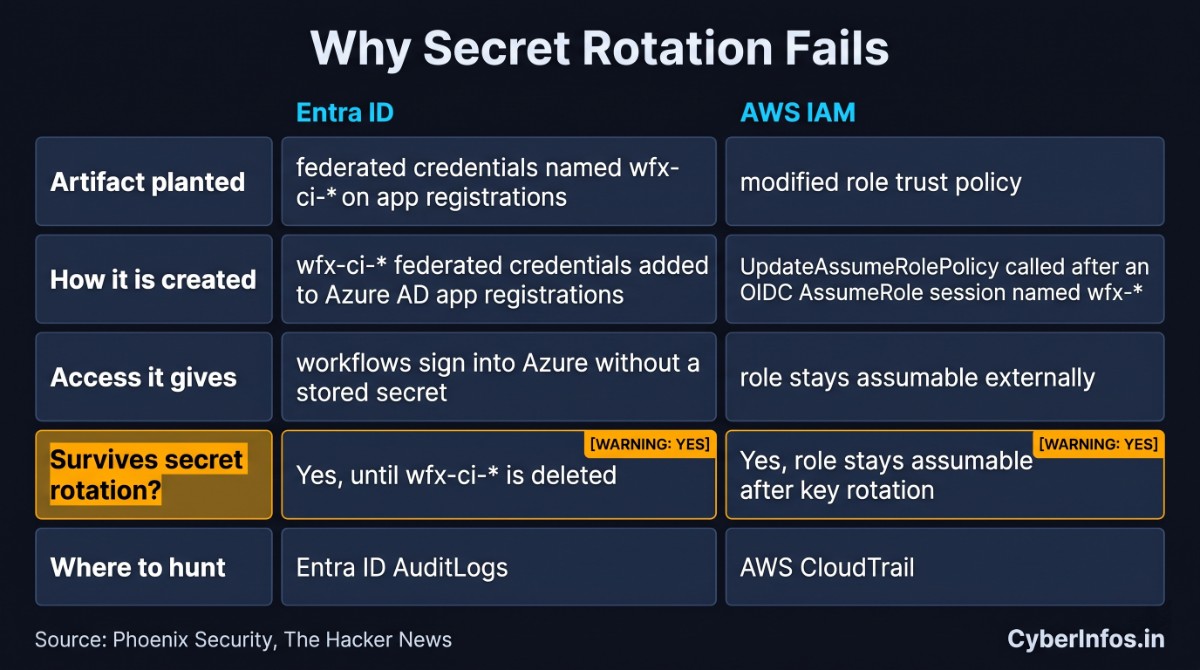
Why Rotating Repository Secrets Alone Will Not Evict the Attacker
- Federated Credentials Bypass Rotation: Per Phoenix Security, a wfx-ci federated identity backdoor uses OIDC tokens rather than secrets, so it survives rotation until
wfx-ci-*is deleted. - Modified AWS Roles Allow External Access: Roles altered by UpdateAssumeRolePolicy remain assumable externally after key rotation.
- Reverted Commits Hide Evidence: Because wfx reverts its commit within minutes, teams must inspect
git log --all --full-historyand cloud logs.
CyberInfos Analyst Insight
- CyberInfos Assesses That the 1,000x GhostAction Overlap Proves Unrotated Developer Tokens Are a Chronic Liability: Reusing October GhostAction victims across November’s 4,837 hijacked developer accounts shows that cleaning malicious YAML without revoking the underlying developer tokens all but guarantees re-compromise.
- From a Defensive Perspective, OIDC Trust Mutation Turns Passwordless CI/CD Into a Backdoor: A two-minute OIDC session is enough to call UpdateAssumeRolePolicy in AWS and add
wfx-ci-*federation in Entra ID. That turns identity federation against the people defending the cloud. - Collaborator Sprawl Multiplies Supply-Chain Risk: Opening 10,431 pull requests through external collaborator access shows how one compromised contributor token can expose dozens of partner organizations.
Indicators of Compromise and Hunting Telemetry
Defenders across GitHub, AWS, Azure, GCP, and Vault should hunt for the verified indicators published by Aikido, SafeDep, The Hacker News, and Chainguard. The table below lists all verified indicators, including AWS AssumeRole trust policy persistence and Entra ID federation artifacts.
| Indicator Type | Value / Pattern | Description and Context |
|---|---|---|
| GitHub Branch & PR Probe | Branch wfx-docs or PR titled docs: dependency audit notes |
Initial write-access probe opened across 61,764+ repos by the wfx GitHub Actions secret stealer per Chainguard |
| Microsoft Entra ID | Federated credentials named wfx-ci-* on App Registrations |
OIDC backdoor allowing secretless Azure login per The Hacker News |
| AWS CloudTrail | AssumeRoleWithWebIdentity / AssumeRole sessions wfx-*, then CreateAccessKey or UpdateAssumeRolePolicy |
Indicates OIDC exchange, IAM key creation, and trust-policy backdooring |
| GCP & Vault Logs | GCP GenerateAccessToken / SignJwt from GitHub pool; Vault JWT logins from GitHub OIDC |
Cross-cloud pivoting from compromised runners |
| Bot & Package Artifacts | wdio-bot commits (28 WebdriverIO repos); Packagist digitalelvis/neuronai-studio 3.14 |
Verified downstream supply-chain artifacts |
Use the following SIEM queries (labeled Draft for testing, not production-validated) to hunt AWS CloudTrail and Entra ID logs:
/* Splunk SPL (Draft for testing, not production-validated):
   Hunt AWS CloudTrail for wfx-* OIDC AssumeRole sessions and follow-on IAM persistence (CreateAccessKey / UpdateAssumeRolePolicy) */
index=aws sourcetype="aws:cloudtrail"
(eventName IN ("AssumeRoleWithWebIdentity", "AssumeRole", "CreateAccessKey", "UpdateAssumeRolePolicy"))
(requestParameters.roleSessionName="wfx-*" OR userIdentity.arn="*wfx-*" OR eventName IN ("CreateAccessKey", "UpdateAssumeRolePolicy"))
| stats count earliest(_time) as first_seen latest(_time) as last_seen values(eventName) as events values(requestParameters.roleName) as roles values(requestParameters.userName) as target_users by sourceIPAddress, userIdentity.arn, awsRegion
| sort - count
// Microsoft Sentinel / Defender KQL (Draft for testing, not production-validated):
// Hunt Microsoft Entra ID AuditLogs for rogue wfx-ci-* federated identity credentials added to App Registrations
AuditLogs
| where TimeGenerated >= datetime(2026-11-10T00:00:00Z)
| where Category == "ApplicationManagement"
| where OperationName has_any ("Update application", "Add federated identity credential", "Add service principal credentials")
| where tostring(TargetResources) has "wfx-ci-"
| project TimeGenerated, OperationName, InitiatedBy, TargetResources, Result, CorrelationId
| order by TimeGenerated desc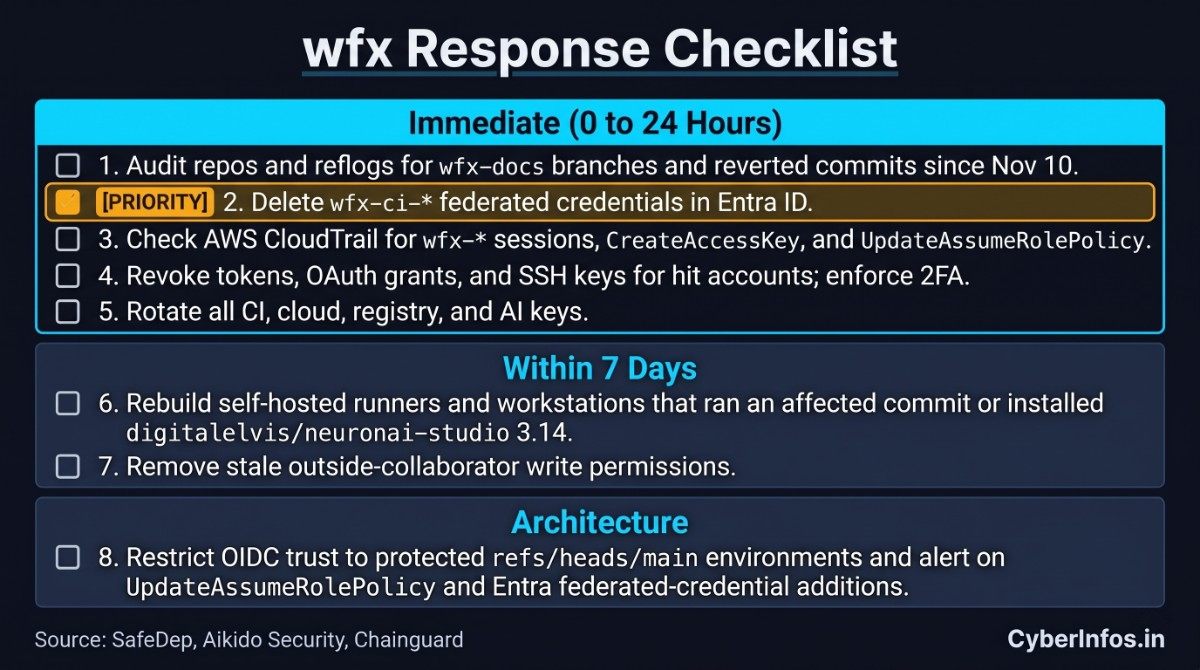
Recommended Actions
Work through these numbered steps in three phases, per SafeDep, Aikido, and Chainguard.
Immediate Actions (0 to 24 Hours)
- Audit Repos for wfx-docs and Reverted Commits: Search repos and reflogs for wfx-docs branches, docs: dependency audit notes PRs, or commits reverted since Nov 10. Treat any account that opened a wfx-docs PR as compromised.
- Evict wfx-ci-* Entra and wfx-* AWS Backdoors: Delete any wfx-ci federated identity backdoor (
wfx-ci-*) in Entra ID. Check AWS CloudTrail forwfx-*sessions plus CreateAccessKey or UpdateAssumeRolePolicy, and audit GCP and Vault logs. - Revoke Tokens and Rotate Secrets: Revoke personal access tokens, OAuth grants, and SSH keys for hit accounts, enforce 2FA, and rotate all CI, cloud, registry, and AI keys (OpenAI, Anthropic, Cursor, Copilot).
Short-Term Actions (Within 7 Days)
- Rebuild Self-Hosted Runners and Exposed Workstations: Decommission and rebuild any self-hosted runner or machine that executed an affected commit or installed digitalelvis/neuronai-studio 3.14.
- Prune External Collaborator Write Access: Remove stale outside-collaborator write permissions across organization repositories.
Long-Term Actions (Architecture)
- Enforce Protected OIDC Subject Claims and Real-Time Trust Alerts: Restrict cloud OIDC trust policies to protected refs/heads/main environments, and alert on any UpdateAssumeRolePolicy call or Entra federated-credential addition.
Global Regulatory and Compliance Implications (USA, UK, Australia, EU, Canada, India)
Regulatory duties apply only when an organization is in scope and suffers a reportable incident. The table below summarizes verified compliance rules across six jurisdictions as of November 13, 2026.
| Jurisdiction | Regulatory Framework | When It Applies and Verified Obligations |
|---|---|---|
| United States | BOD 22-01, SEC 8-K, CIRCIA | When It Applies: Today (November 13, 2026) is the mandatory BOD 22-01 federal deadline for Barracuda ESG CVE-2026-116606 and CVE-2026-111560 in CISA KEV per The Hacker News. U.S. public issuers file SEC Form 8-K Item 1.05 within 4 business days of materiality (Form 6-K for foreign issuers per AOPL). CIRCIA 72h/24h clocks await CISA’s final rule (RIN 1670-AA04). |
| United Kingdom | UK GDPR (ICO) & NCSC CAF | When It Applies: Personal data breaches via stolen cloud tokens require 72-hour ICO notice under UK GDPR Art. 33; essential services follow UK NCSC CAF. |
| Australia | SOCI Act, OAIC NDB, Essential Eight | When It Applies: SOCI Act entities report to ASD within 12h (critical) or 72h, notify OAIC for eligible breaches, and enforce MFA and privileged access rules under Essential Eight. |
| European Union | NIS2, EU GDPR, EU CRA | When It Applies: NIS2 requires 24h warning, 72h notice, and 1-month final report; EU GDPR sets a 72h breach notice. EU CRA 24h/72h rules (active Sep 11, 2026 per Global Compliance Map) bind software manufacturers. |
| Canada | PIPEDA | When It Applies: PIPEDA breaches posing real risk of significant harm must be reported as soon as feasible (no fixed hour window). |
| India | CERT-In, DPDP Rules 2025, RBI/SEBI | When It Applies: CERT-In mandates 6-hour reporting and 180-day log retention per AOPL. Under DPDP Rules, 2025 per WONE Global, Consent Manager registration rules (Rule 4) officially take effect today, November 13, 2026, while main breach rules take effect May 13, 2027. RBI / SEBI set 6-hour rules. |
This summary supports operational readiness and is not legal advice.
Frequently Asked Questions (FAQ)
What is the wfx GitHub Actions secret stealer and how many accounts were compromised?
The wfx GitHub Actions secret stealer (wfx-loot) is an automated supply-chain campaign that Aikido Security and SafeDep disclosed on November 12, 2026. Starting November 10, an attacker used stolen credentials for 4,837 GitHub accounts to probe 61,764+ repositories, push malicious commits to 8,093 repositories, and harvest CI/CD and cloud secrets from at least 1,806 to 1,835 repositories, per The Hacker News.
How are the hijacked developer accounts connected to October’s GhostAction wave?
Aikido Security’s analysis, reported by The Hacker News and Barrier Networks, shows that the 4,837 hijacked developer accounts overlap heavily with victims of October’s GhostAction campaign. Those victims were roughly 1,000 times more likely to be reused this week. Researchers have not, however, attributed both waves to the same threat actor.
How can repository owners detect if they were targeted by the wfx campaign?
Chainguard advises defenders to search all repositories and Git reflogs for a wfx-docs pull request probe titled docs: dependency audit notes from a branch named wfx-docs. They should also inspect deleted or reverted workflow commits between November 10 and November 13, 2026.
Why does rotating GitHub secrets fail to remove the Azure Entra ID backdoor?
During execution, the stealer exchanges GitHub OIDC tokens to plant a wfx-ci federated identity backdoor (wfx-ci-*) on Azure AD application registrations, per Phoenix Security. Federated identity credentials authenticate workflows with OIDC tokens rather than stored secrets, so attackers keep Azure access until the rogue wfx-ci-* federation entry is deleted.
How does the wfx payload maintain access inside Amazon Web Services environments?
In AWS environments, the malware establishes AWS AssumeRole trust policy persistence by exchanging a GitHub OIDC token for an AssumeRoleWithWebIdentity session named wfx-*. It then calls CreateAccessKey to mint permanent IAM user keys and UpdateAssumeRolePolicy to open the IAM role’s trust policy to external AWS accounts, per The Hacker News.
Final Thoughts
The rapid spread of the wfx GitHub Actions secret stealer is a wake-up call for every engineering team that relies on CI/CD automation and cloud OIDC federation. The payload reverts its commits within minutes and rewrites AWS IAM trust policies and Azure Entra ID federated credentials (wfx-ci-*). Merely rotating repository variables leaves your cloud accounts exposed.
Audit GitHub logs for wfx-docs branches and reverted runs immediately. Remove unauthorized wfx-ci-* Entra ID credentials and modified AWS role trust policies, and revoke unrotated GhostAction tokens. Share your findings in the comments below, and subscribe to CyberInfos.in for daily verified threat intelligence.
