
Nearly a thousand Zyxel GS1900 switches across 48 countries have already been compromised through a single unpatched flaw. The campaign that started in mid-August is still running. At the center of it is CVE-2026-7273, a stack-based buffer overflow in the GS1900 series’ web-management CGI program. It lets an unauthenticated attacker on the local network run operating system commands simply by sending a malformed HTTP request.
Zyxel shipped a fix in June 2026. But by the time a suspected Chinese-speaking threat actor began mass-exploiting the Zyxel GS1900 vulnerability on August 17, thousands of switches were still running unpatched firmware.
On September 21, CISA added CVE-2026-7273 to its Known Exploited Vulnerabilities (KEV) catalog, giving federal agencies a hard deadline to patch or pull the devices offline.
Here’s what network admins and MSPs actually need to know: how the attack chain works, what data has already been stolen, and the hardening steps worth running through this week rather than filing away for later.
Quick Answer
CVE-2026-7273 is a stack-based buffer overflow (CVSS 8.8) in Zyxel GS1900 series switches that lets an unauthenticated LAN attacker execute OS commands via a crafted HTTP request. Zyxel patched it in June 2026, but a Chinese-speaking threat actor has exploited it since August 17 to steal credentials and configuration data from 996 switches across 48 countries. CISA added it to the KEV catalog on September 21, 2026.
What Is CVE-2026-7273?
CVE-2026-7273 is a stack-based buffer overflow (CWE-121) in the CGI program that powers the web-management interface of Zyxel’s GS1900 Smart Managed Switches. The CGI code fails to validate the length of input before writing it into a fixed-size stack buffer. A specially crafted HTTP POST request can overwrite adjacent memory and hijack program execution.
Here’s what makes this Zyxel switch exploit so easy to weaponize: the flaw sits in the switch’s LAN-facing management service, so an attacker needs only local network access, not valid credentials, to trigger it. Successful exploitation grants OS-level command execution. In practice, that’s full control of the switch. The National Vulnerability Database rates CVE-2026-7273 at 8.8 (High) on the CVSS scale, reflecting low attack complexity and no privileges required.
Which Zyxel GS1900 Models Are Affected?
Zyxel’s advisory for CVE-2026-7273 lists firmware versions 2.90(XXXX.1)C0 and earlier as vulnerable across the GS1900 line, including the GS1900-8, GS1900-8HP, GS1900-10HP, GS1900-16, GS1900-24, GS1900-24E, GS1900-24EP, GS1900-24HPv2, GS1900-48, and GS1900-48HPv2.
These are entry-level Gigabit Ethernet switches marketed at small offices, schools, hotels, and retail locations. That matters, because it’s exactly the kind of environment where IT staffing is thin and management interfaces often stay exposed on default settings. Zyxel released patched firmware, version 2.90(XXXX.2)C0, for the affected models on June 16, 2026, as part of a broader Zyxel security update for the GS1900 line.
Timeline: From Patch to Mass Exploitation
The gap between disclosure and exploitation is the real story here.
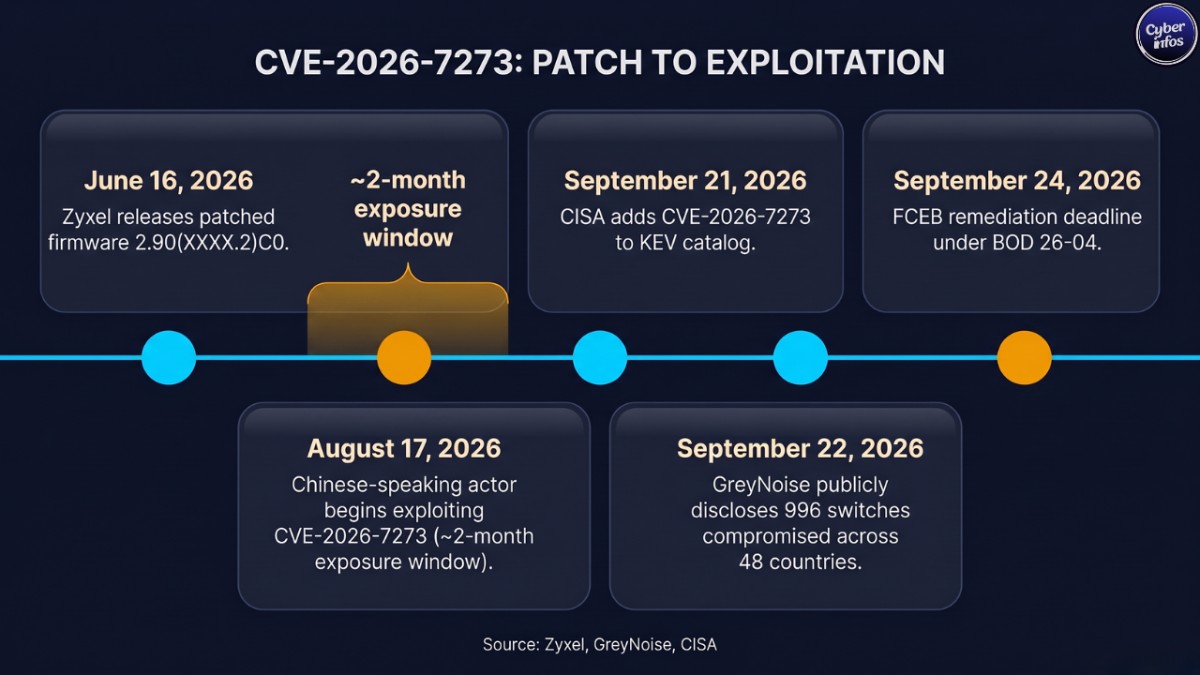
Zyxel privately received the vulnerability report and shipped a fix on June 16, 2026. Nothing public suggested active abuse for roughly two months. Then, according to threat intelligence firm GreyNoise, a suspected Chinese-speaking malicious cyber actor began exploiting CVE-2026-7273 on or around August 17, 2026, and kept the campaign running until GreyNoise flagged it publicly on September 22. CISA added the CVE to its KEV catalog on September 21, confirming the first publicly documented in-the-wild exploitation of this specific vulnerability.
None of this happens in a vacuum. The two-month-plus window between patch availability and detected mass exploitation is a familiar pattern. Research from Eclypsium and the Verizon 2025 DBIR both point to an eight-fold increase in exploitation targeting network edge devices such as switches, routers, and VPN appliances, with a median patch time that regularly exceeds 30 days even after a fix ships.
Anatomy of the Attack Chain
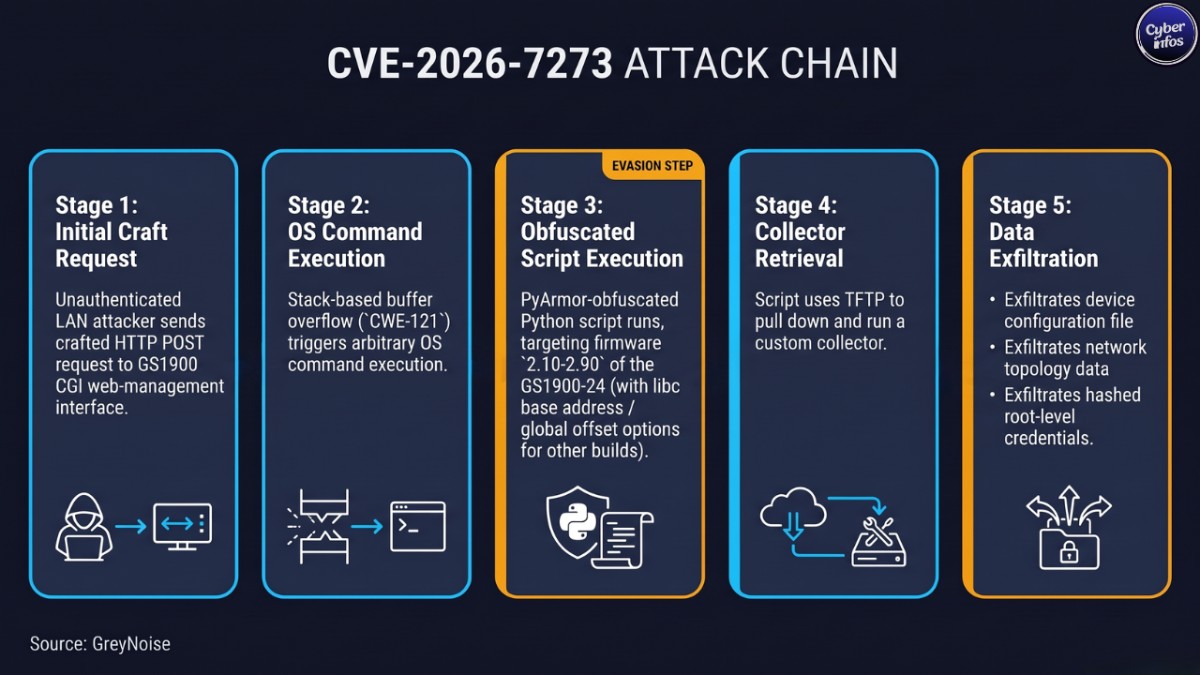
GreyNoise’s analysis describes a methodical, automated operation, not opportunistic scanning. The attacker’s exploit code was packaged in a Python script obfuscated with the commercial tool PyArmor, which made static analysis harder for defenders who captured a sample.
Once deobfuscated, researchers found the script explicitly targeting firmware versions 2.10 through 2.90 of the GS1900-24. It also exposed command-line options (libc base address, global offset values) that let the operator retarget the same exploit against other firmware builds in scope for the vulnerability.
What happened after the initial break-in is the part worth paying attention to. After gaining command execution, the attacker used TFTP to pull down and run a custom collector script, then exfiltrated each switch’s configuration file, network topology information, and hashed root-level credentials.
GreyNoise also linked this activity to a threat cluster that overlaps with a group Acronis separately reported abusing a Gitea vulnerability, CVE-2026-60004. That overlap suggests the same actor is running exploitation campaigns across multiple unrelated products in parallel.
CyberInfos Analyst Insight
Two details in this campaign matter more than the headline device count.
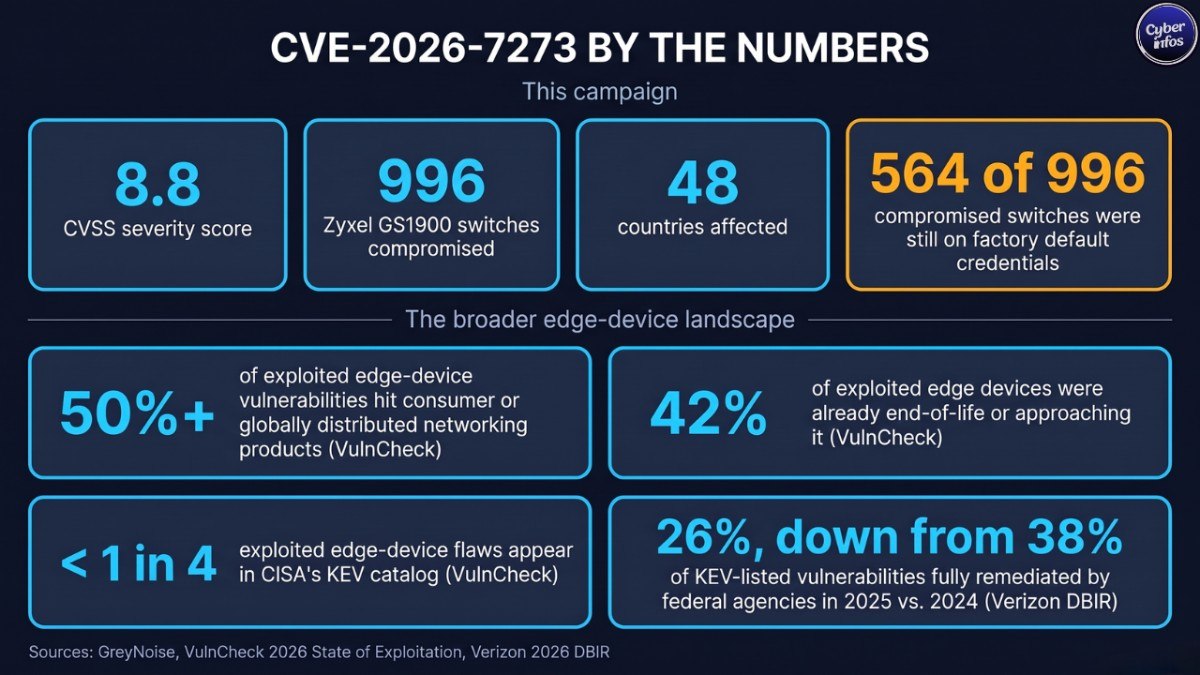
First, GreyNoise found that 564 of the 996 compromised switches were still running factory default credentials. That means the buffer overflow wasn’t even the only way in; default logins alone would have handed over the management interface. That single fact says more about real-world network hygiene than any awareness statistic could.
Second, the exploit script’s built-in options for targeting other firmware builds suggest this isn’t a one-off tool built for a single campaign. It’s reusable infrastructure that the same actor, or others who obtain the script, can point at any exposed GS1900 switch running outdated firmware, indefinitely.
CyberInfos assesses that switches and other “invisible” network infrastructure remain under-monitored relative to servers and endpoints in most SOC programs. This campaign is a direct consequence of that blind spot, not a failure of Zyxel’s patch itself, which had been available for over two months before exploitation began.
Why Network Switches Keep Getting Hit
Switches, routers, and other edge devices are attractive targets for a simple reason. They sit at the boundary between internal and external traffic, they’re rarely instrumented with endpoint detection, and they often run for years without a firmware check.
VulnCheck’s 2026 State of Exploitation research on network edge devices found that consumer and globally distributed networking products account for over half of all exploited edge-device vulnerabilities, and that roughly 42% of exploited edge devices were already end-of-life or approaching it.
Here’s the part that should worry defenders leaning on federal advisories alone: the same research found that fewer than one in four exploited edge-device flaws even appear in CISA’s KEV catalog, meaning organizations relying solely on that feed for prioritization for network switch security are missing most of the risk.
GS1900 switches fit the profile precisely. They’re inexpensive, widely deployed in small business and hospitality settings, and easy to forget once installed.
CISA KEV Listing and the BOD 26-04 Deadline
CISA added CVE-2026-7273 to its Known Exploited Vulnerabilities catalog on September 21, 2026, and set a remediation deadline of September 24 for Federal Civilian Executive Branch (FCEB) agencies under Binding Operational Directive 26-04.
BOD 26-04, issued in June 2026, compresses the federal patch window to as little as three days for vulnerabilities that combine public exposure, automated exploitability, full system control, and confirmed active exploitation. All four of those criteria apply here. The directive applies only to FCEB agencies, but CISA explicitly encourages every organization to treat CISA KEV entries as a prioritization signal regardless of sector.
Why the urgency? The 2026 Verizon DBIR found only 26% of KEV-listed vulnerabilities were fully remediated by federal agencies in 2025, down from 38% the year before. Against that backdrop, the compressed timeline reads less like a formality and more like a forcing function.
Real-World Impact
The real-world fallout from CVE-2026-7273, this Zyxel GS1900 vulnerability, is already measurable. GreyNoise reports the compromised switches are concentrated in Italy, the United States, Taiwan, South Korea, and several EU member states, spanning 48 countries in total.
The attacker exfiltrated device configuration files, network topology data, and hashed root credentials from 996 switches. That data provides a ready-made map of internal network layout and a foothold for lateral movement or follow-on credential cracking, even without further exploitation of the switches themselves.
Because GS1900 switches are common in small offices, schools, hotels, and retail environments, the affected organizations are disproportionately smaller entities without dedicated network security teams. That likely explains both the scale of unpatched devices and the number still using default credentials months after a fix was available.
Network Switch Hardening Checklist
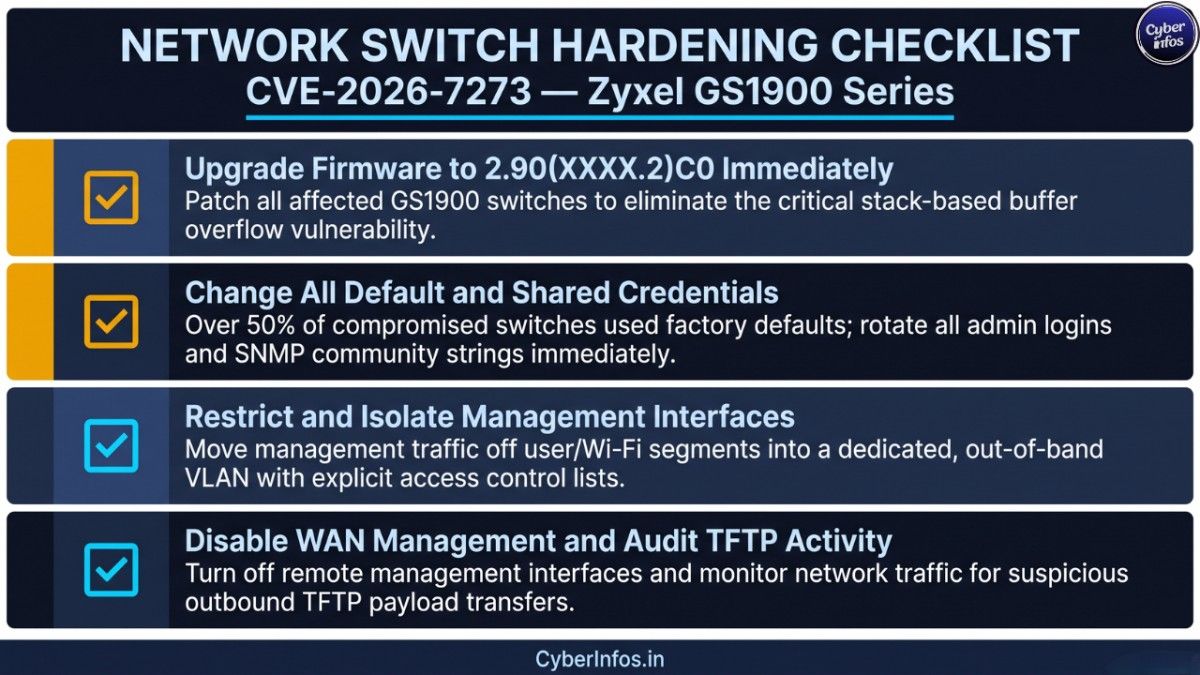
- Identify every GS1900 switch on your network and confirm the firmware version against Zyxel’s advisory
- Upgrade to firmware 2.90(XXXX.2)C0 or later on all affected models immediately
- Change every default or shared admin credential on network switches, not just this model
- Remove the switch management interface from any network segment reachable by general users or guest Wi-Fi
- Restrict management access to a dedicated out-of-band or admin-only VLAN with an explicit allow-list
- Disable remote/WAN management on switches unless there is a documented business need
- Enable logging on switch management interfaces and forward it to your SIEM if the device supports it
- Rotate any credentials or SNMP community strings that may have been exposed if a switch was running default credentials
- Check outbound TFTP activity from switch management VLANs, since the observed campaign used TFTP to pull a secondary payload
- Build a firmware-review cadence for edge devices (switches, routers, and firewalls) rather than treating them as install-and-forget hardware
FAQ
What is CVE-2026-7273?
CVE-2026-7273 is a stack-based buffer overflow in the CGI web-management program of Zyxel GS1900 series switches. It lets an unauthenticated attacker on the local network execute operating system commands by sending a specially crafted HTTP request, and it carries a CVSS score of 8.8.
Which Zyxel switch models are vulnerable to CVE-2026-7273?
The flaw affects ten GS1900 models, including the GS1900-8, GS1900-8HP, GS1900-10HP, GS1900-16, GS1900-24, GS1900-24E, GS1900-24EP, GS1900-24HPv2, GS1900-48, and GS1900-48HPv2, running firmware 2.90(XXXX.1)C0 or earlier.
Has Zyxel released a patch for CVE-2026-7273?
Yes. Zyxel published patched firmware, version 2.90(XXXX.2)C0, for all affected GS1900 models on June 16, 2026, more than two months before mass exploitation began.
Is CVE-2026-7273 being actively exploited?
Yes. GreyNoise reported that a suspected Chinese-speaking threat actor began exploiting CVE-2026-7273 on August 17, 2026, compromising 996 switches across 48 countries and exfiltrating configuration data and hashed credentials.
Why was CVE-2026-7273 added to the CISA KEV catalog?
CISA added it on September 21, 2026, after confirming evidence of active exploitation, which is the standard criteria for inclusion in the Known Exploited Vulnerabilities catalog.
What is the CISA deadline for patching CVE-2026-7273?
Under Binding Operational Directive 26-04, Federal Civilian Executive Branch agencies were required to remediate CVE-2026-7273 by September 24, 2026. Private organizations face no legal deadline but are encouraged to treat KEV listings with the same urgency.
What data did attackers steal from compromised Zyxel switches?
According to GreyNoise, the attacker exfiltrated each switch’s configuration file, network topology information, and hashed root-level credentials using a custom collector script delivered over TFTP.
How many of the compromised switches used default credentials?
GreyNoise found that 564 of the 996 compromised switches were still using factory default credentials at the time of compromise, giving attackers a second way in beyond the buffer overflow itself.
Is this attack linked to other recent campaigns?
GreyNoise noted overlaps between this threat actor and a cluster that Acronis separately reported exploiting a Gitea vulnerability, CVE-2026-60004, suggesting shared infrastructure or the same operator running multiple concurrent campaigns.
How can I tell if my Zyxel GS1900 switch has been compromised?
Check the current firmware version against Zyxel’s advisory, review switch configuration and admin accounts for unexpected changes, look for unusual outbound TFTP traffic from the management VLAN, and rotate credentials immediately if the device was ever left on factory defaults.
Final Thoughts
CVE-2026-7273 is a reminder that a patch’s existence doesn’t equal protection. Zyxel shipped a fix in June, yet nearly a thousand switches across 48 countries were still exposed and exploited two months later, hundreds of them behind nothing more than a default password.
The immediate action is straightforward: confirm your GS1900 firmware version, patch to 2.90(XXXX.2)C0 or later, and eliminate default credentials network-wide. The longer-term fix is cultural. Bring switches, routers, and other edge infrastructure into the same patch-management and monitoring cadence as servers and endpoints, because attackers have clearly already made that shift.
